If phase-2 negotiation is failing due to TS unacceptable error(TS_UNACCEPTABLE), it means there is mismatch between traffic selector configured between VOS and remote IPsec peer device.
Use CLI 'show orgs org-services <org-name> ipsec vpn-profile <vpn-profile-name> ipsec history' to find phase-2 negotiation issues
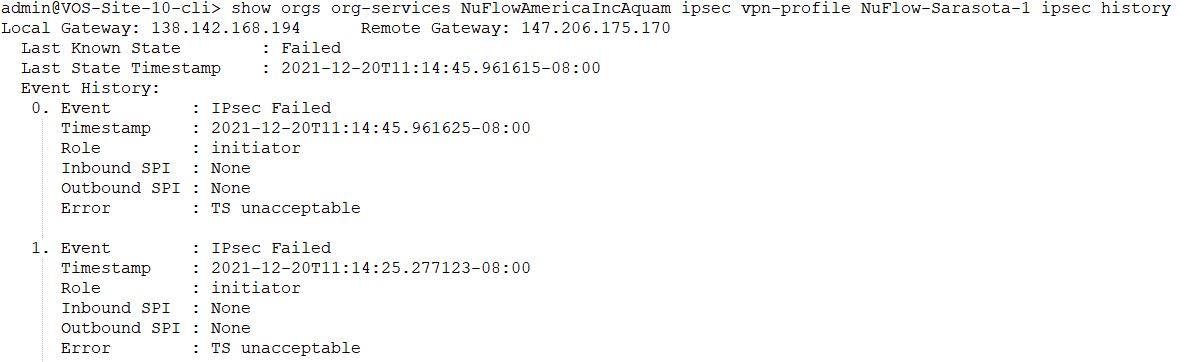
This issue happens in following scenarios:
Scenario-1:
Route based IPsec is configured on one side and policy based IPsec is configured on other side.
Scenario-2:
Policy configured on local IPsec device should match on remote IPsec device by reversing source and destination on remote device. For example:
If policy is configured with source subnet as 192.168.10.0/24 and destination as 172.16.10.0/24 on local IPsec device but remote IPsec peer is not configured as source subnet 172.16.10.0/24 and destination as 192.168.10.0/24, TS unacceptable(TS_UNACCEPTABLE) will be seen.