Problem Description:
Unable to login using TACACS authentication into Versa Director after upgrading the device to 20.X release.
Solution:
From 20.X release, we need to configure service name manually to match with TACACS config as below.
group = ProviderDataCenterSystemAdminGroup {
login = PAM
service = test {
Versa-Role = "ProviderDataCenterSystemAdmin"
Versa-GUI-Idle-TimeOut = "300"
}
}
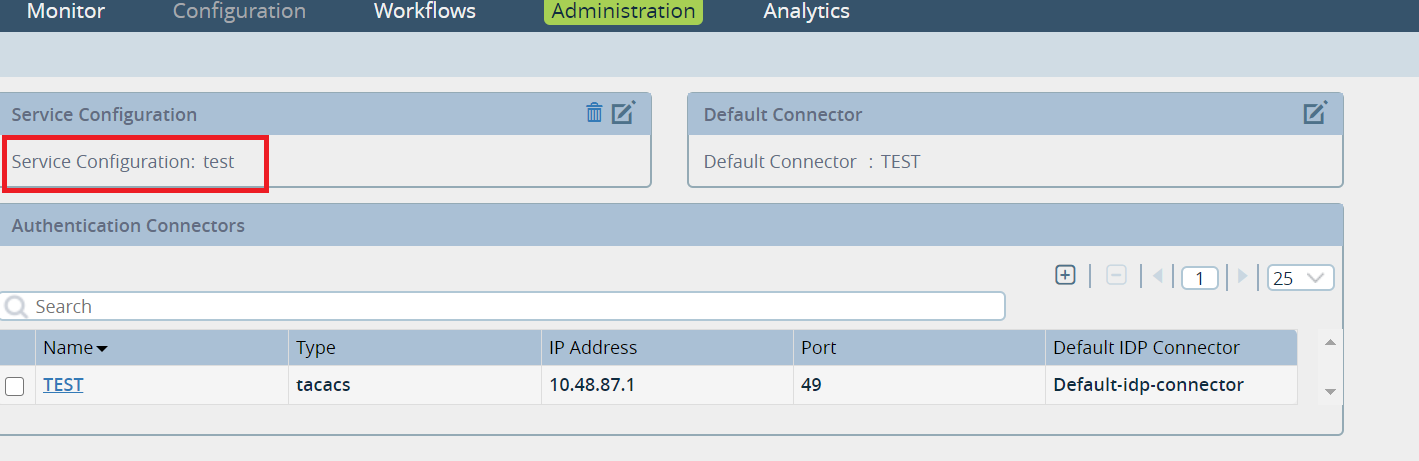
Vnms Extenal logs:
08/04/2020 13:06:26,359 Tacacs service name : "" ========> If you see this empty, then you should configure service name manually as shown above
08/04/2020 13:06:27,787 10.192.148.1 server is reachable for user Tom
08/04/2020 13:06:27,793 versaTenant:
08/04/2020 13:06:27,794 versaRole:
08/04/2020 13:06:27,795 userid: 1002
08/04/2020 13:06:27,796 groupid: 1000
08/04/2020 13:06:27,798 GUI-Idle-TimeOut(mins): 15
08/04/2020 13:06:27,799 Versa-Multi-Tenant-Roles:
08/04/2020 13:06:27,801 failed to login