Overview
Versa Cloud Access Security Broker (CASB) is a security enforcement component integrated into the Versa SASE (Secure Access Service Edge) platform. It provides visibility, compliance monitoring, threat protection, and granular policy control for cloud application usage across enterprise environments.
Versa CASB works inline with Versa SD-WAN and SSE traffic flows, allowing enforcement directly at the network layer without requiring separate appliances or endpoint agents.
Key Features
Versa CASB provides the following capabilities:
- Cloud application discovery and Shadow IT detection
- Granular access control based on:
- Application
- User
- Device
- Activity type
- Deep inspection through SSL decryption
- Upload/download control for SaaS applications
- Threat protection and compliance enforcement
- Managed and unmanaged device visibility
Supported Deployment Modes
1. Inline (Forward Proxy) – Supported
Traffic flows through the Versa gateway where real-time inspection and enforcement are applied.
Requirements:
- SSL decryption must be enabled for HTTPS traffic inspection.
2. Out-of-Band (API Mode) – Not Yet in Production
Currently not available in production.
3. Reverse Proxy – Not Yet in Production
Currently not available in production.
Recommendation: Inline mode provides the most complete enforcement capability and is recommended for managed devices.
Software Requirements
- Versa VOS: 22.1.x or later (21.2.x minimum for basic CASB)
- Versa Director: 22.1.x or later
Network Prerequisites
Before enabling Versa CASB, ensure the following:
- SSL inspection is fully functional
- DNS resolution is working on the Versa gateway
- URL filtering databases are updated
- App-ID / IPS signature databases are updated
Configuration Steps
Step 1: Enable SSL Inspection
CASB inline mode requires TLS decryption to inspect SaaS traffic.
Sample CLI Configuration
set orgs org-services <Org-name> security profiles decrypt Forward decrypt-profile-type ssl-forward-proxy
set orgs org-services <Org-name> security profiles decrypt Forward certificate sarath-ca
set orgs org-services <Org-name> security decryption-policies Test rules R1 set action decrypt
set orgs org-services <Org-name> security decryption-policies Test rules R1 set decryption-profile Forward
Step 2: Create CASB Profile
Define the cloud applications and activities to allow or block.
Supported controls may include:
- File upload
- File download
- Post
- Like
- Chat
- Share
- Other application-specific activities
Sample CLI Configuration
set orgs org-services <org-name> security profiles casb CASBGMIALGPT default-action predefined allow
set orgs org-services <org-name> security profiles casb CASBGMIALGPT lef-profile-default true
set orgs org-services <org-name> security profiles casb CASBGMIALGPT rules Gmil-Chatgpt match predefined-applications chatgpt predefined-application-activity [ upload_file ]
set orgs org-services <org-name> security profiles casb CASBGMIALGPT rules Gmil-Chatgpt match predefined-applications gmail predefined-application-activity [ send upload_file ]
set orgs org-services <org-name> security profiles casb CASBGMIALGPT rules Gmil-Chatgpt set action predefined block
Step 3: Apply CASB Profile to Security Policy
CASB profile must be mapped to the access policy rule.
Important: IPS App-ID detection must be enabled because CASB uses DPI/App-ID to detect user actions inside SaaS applications.
Without App-ID, granular actions such as:
- Allow Dropbox download
- Block Dropbox upload
cannot be enforced.
Enable IPS based App-ID Detection
set orgs org-services <org-name> security ips appid-detection enable true
set system parameters ips-appid-detection enabled
Sample Access Policy
set orgs org-services <org-name> security access-policies Default-Policy rules CASB match source user local-database status disabled
set orgs org-services <org-name> security access-policies Default-Policy rules CASB match source user external-database status disabled
set orgs org-services <org-name> security access-policies Default-Policy rules CASB match source user group-mapping-profile AD-SULAI
set orgs org-services <org-name> security access-policies Default-Policy rules CASB match source user group CN=PS,CN=Groups,DC=versaps,DC=com description PS
set orgs org-services <org-name> security access-policies Default-Policy rules CASB match source user user-type selected
set orgs org-services <org-name> security access-policies Default-Policy rules CASB set security-profile ips predefined-ips-profile "Versa Recommended Profile"
set orgs org-services <org-name> security access-policies Default-Policy rules CASB set security-profile casb user-defined-casb-profile CASBGMIALGPT
set orgs org-services <org-name> security access-policies Default-Policy rules CASB set action allow
Versa CASB provides inline cloud application security with granular activity control. Proper deployment requires:
- SSL Inspection
- CASB Profile
- IPS App-ID
- Security Policy Mapping
Once configured correctly, organizations can control SaaS application usage such as blocking uploads while allowing downloads.
Director and Concerto Deployment Notes
If Using Concerto
The required IPS profile for CASB is automatically pushed when CASB policy is deployed.
If Using Versa Director
You must manually:
- Create IPS profile
- Include signatures for app-activity class type
- Apply IPS profile to CASB rule
Useful Reference
Versa Documentation:
Troubleshooting
Verify Policy Hits
Use the following command to confirm traffic is matching the CASB profile:
show orgs org-services <Org-Name> security profiles casb statistic
Eg Output:
admin@CHN-SSE-GW1-cli> show orgs org-services DEMOORG-SSE security profiles casb statistics
DEFAULT RULE
PROFILE ACTION HIT
PROFILE NAME HIT CNT HIT CNT RULE NAME CNT
----------------------------------------------------------------------------------------
CASB 0 0 LINKEDIN 0
CASB-P1 0 0 YOU-GMAIL 0
CASBGMIALGPT 56 0 Gmil-Chatgpt 56
GMAIL 0 0 GMAIL 0
Gemini-Bard 5 0 Bard-Gemini 5
Interpretation:
- 0 hits = traffic not matching policy
- Hit count increasing = traffic successfully inspected
CASB Session Verification in VSMD
To validate whether a CASB policy is functioning correctly for a specific user session, check the live session details in VSMD. This helps confirm:
- SSL decryption status
- Application identification
- Application activity detection
- Policy action applied (allow / drop)
Commands to Verify Specific Session
Step 1: Connect to VSMD
>vsh connect vsmd
Step 2: Find Session ID Using Source IP
>show vsf session all brief | grep <source-ip>
Step 3: Display Detailed Session Information
>show vsf session handle extensive <session-id>
Example Session Analysis
1. SSL Decryption Verification
The below output confirms that SSL decryption is active for this session:
SSL/TLS session information,
Proxy Type: SSL_FORWD_PROXY, Starttls session: NO, Starttls Capability: NO
Tenant-id: 3, Public Key Length: 72, Server Hostname: mail.google.com
Decryption-Profile: TLS
Decryption Policy Details:
Rule: SSL-Decryption, Action: decrypt, Action-Type: NA
Packet count: 0, mbuf count (inward: 2, onward: 0)
Flags: PROTO_DETECTED, APPID_FINAL, URL_LOOKUP_BEGIN, URL_MATCH_FOUND, DECRYPT_STRM_START,
ACTIONS_ENABLED, REQ_PARSED,
Inward:
Version: TLSv1.3, Cipher: TLS_AES_128_GCM_SHA256
Onward:
Version: TLSv1.3, Cipher: TLS_AES_128_GCM_SHA256
Interpretation
- Proxy Type: SSL_FORWD_PROXY = Forward proxy SSL inspection enabled
- Decryption Profile: TLS = TLS decryption profile applied
- Rule: SSL-Decryption = Matching decryption rule
- Traffic is decrypted successfully
2. Application Identification Verification
Vparse Session info:
l7_protos: 211(http) 175(google_gen) 158(gmail)
l7_base_protos: 211(http) 175(google_gen)
appid_flags = 0xfb(classified,final,interim_classified,other_module_done,urlf_reported,qosmos_seen,http_header_end,)
appid reported at c2s direction with 12 c2s pkt and 6 s2c pkt
hold uda id = 0
policy_match_ev = 1
Interpretation
The system successfully identified the application stack as:
- HTTP
- Google Services
- Gmail
This confirms App-ID classification is working properly.
3. Activity Detection Verification
Appid state change:5
c2s:2, s2c:1, Path_end event, base.ip.tcp.ssl(0)
c2s:4, s2c:3, Classified event, base.ip.tcp.ssl.https.google_gen.gmail(0)
c2s:12, s2c:5, Classified event, base.ip.tcp.http.google_gen.gmail(0)
c2s:1288, s2c:855, Transaction event, upload attachment(517)
c2s:1288, s2c:855, Transaction event, compose(513)
Interpretation
The CASB engine detected Gmail user activities:
- Upload Attachment
- Compose Email
This confirms granular activity detection is functioning.
4. CASB Policy Action Verification
current_trans_ix_cts = 42
current_trans_ix_stc = 42
session_action = drop-session
session_action_module = casb_tnt_scanner
decryption policy rule match = 960 (Decrypt)
skip_file_extract = 0
is_cportal_session = false
security-offload-status = Disabled
ips-offload-status = Pending
dlp-offload-status = Don't offload
Transaction Discarded Id = 0
username = tamil
Results: count: 46
Interpretation
- The session was dropped based on configured CASB policy
- Action was enforced by CASB module
This usually indicates upload block / restricted activity policy matched.
User Notification
When the CASB policy blocks the detected activity (for example, Gmail attachment upload), the end user will receive a browser/application notification similar to the screenshot shared.
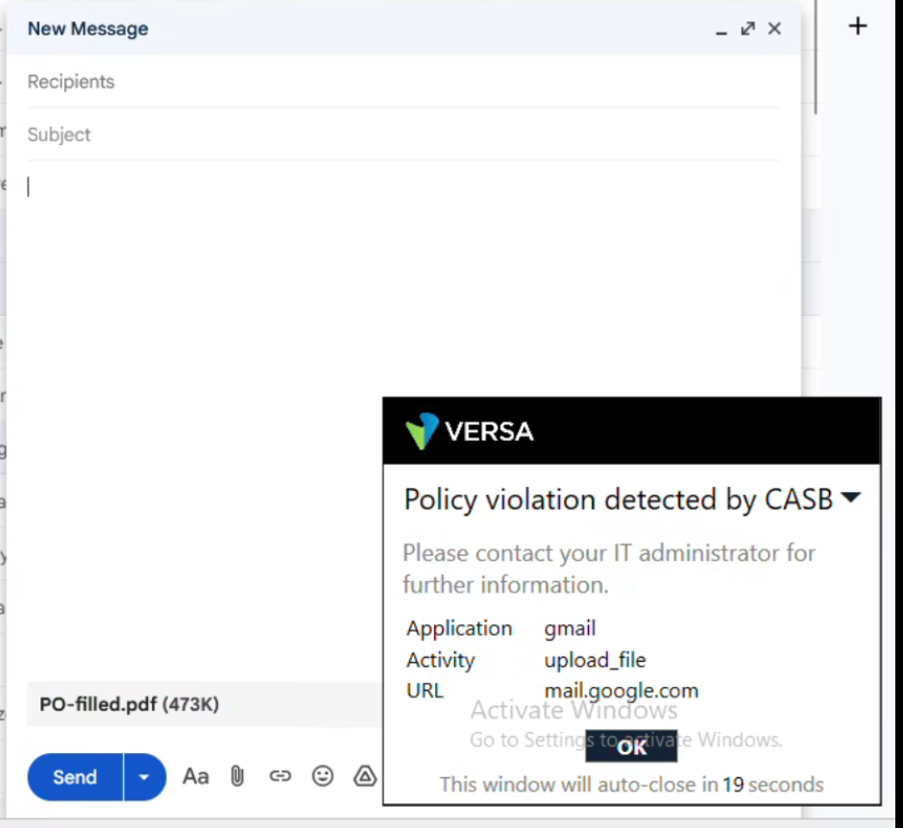
This notification indicates that the requested action was denied based on the organization's security policy.
Enable CASB Debug
% set debug casb all-flags level all
%commit
Enable debug only during troubleshooting, as verbose logging may increase CPU and log volume.
Example Debug Output Analysis
2026-04-30 16:16:54.089 DEBUG [0x104] vs_casb_find_match: CASB rfc matched best rule order = 1
2026-04-30 16:16:54.089 INFO [0x104] vs_casb_find_match: shdl 139625961281028 matched casb rule Gmil-Chatgpt(1), action block ------>Rule name and action
2026-04-30 16:16:54.090 INFO [0x104] vs_casb_inc_rule_stats: Increase rule (tnt 3, profile 1031, rule 1) stats
2026-04-30 16:16:54.090 INFO [0x104] vs_casb_inc_rule_stats: Increase profile (tnt 3, profile 1031) stats
2026-04-30 16:16:54.090 INFO [0x104] vs_casb_tnt_scanner_take_rule_action: shdl 139625961281028 take action from rule Gmil-Chatgpt(1) ------>Taken action based on rule config
2026-04-30 16:16:54.090 DEBUG [0x104] _vs_identity_send_user_notification: alerts: tnt_id:3, sess_hdl:0x7efd33d2d604, client:CASB, saction:(null), src_ip:100.72.0.4, paction:(null), head:(null), message:Access to the web site is blocked at this time. Please contact your administrator for more information., md_app:gmail, md_action:(null), md_reason:(null), md_activity:upload_file, md_url:(null), pd_notif_id:(null) policy_action_obj:block --- > The activity which is being blocked.
2026-04-30 16:16:54.090 DEBUG [0x104] vs_identity_live_user_ip_tbl_find_cb: LPM search
2026-04-30 16:16:54.090 DEBUG [0x104] vs_identity_live_user_ip_tbl_lpm_search: User tamil with IP 100.72.0.4
2026-04-30 16:16:54.090 DEBUG [0x104] _vs_identity_send_user_notification: user type : VSA
2026-04-30 16:16:54.091 DEBUG [0x104] vs_identity_alerts_get_def_action: found matching rule 'Gmail'
2026-04-30 16:16:54.091 DEBUG [0x104] vs_identity_alerts_get_def_action: action : 404
2026-04-30 16:16:54.091 DEBUG [0x104] vs_identity_alert_send_vsa_notif: keystr : CASB:u:u:gmail:upload_file:u
2026-04-30 16:16:54.105 DEBUG [0x104] vs_identity_alert_ctxt_exist: for tnt_id:3, src_ip:100.72.0.4, keystr:CASB:u:u:gmail:upload_file:u
2026-04-30 16:16:54.106 DEBUG [0x104] vs_identity_alert_ctxt_lookup: for tnt_id:3, src_ip:100.72.0.4, keystr:CASB:u:u:gmail:upload_file:u, del_expired:true
2026-04-30 16:16:54.106 DEBUG [0x104] vs_identity_alert_ctxt_exist: ctxt not exist
2026-04-30 16:16:54.106 DEBUG [0x104] vs_identity_alert_send_vsa_notif: cp_url : https://captiveportal.versanow.net:44991/versa-flexvnf/alerts/index.htm?key=CASB%3au%3au%3agmail%3aupload_file%3au
Note: After you capture the debug output, please make sure to delete the same using below command.
% delete debug casb all-flags level all
%commit
Common Issues
CASB Rule Not Triggering
Check:
- Security policy order
- User/group match conditions
- SSL decryption status
- App-ID detection enabled
- Correct SaaS application selected
Upload Block Not Working
Check:
- IPS profile attached
- Application activity signature present
- Traffic decrypted successfully
Best Practices
- Always deploy SSL inspection before CASB.
- Use least-privilege activity controls.
- Monitor hit counters after policy deployment.
- Keep App-ID and URL databases updated.
- Start with audit mode before full block mode.